 Defender XDR
ISOC Is a Licence Change in an Agentic Costume (And That's Actually Good News)
All right class.
You've got E5. You've got Defender filling the incident queue before your first coffee. You haven't got Sentinel, because
Topic
Security Operations
Running security operations on Sentinel and Defender: choosing an MSSP, life after go-live, the settings that matter and what a SOC should own.
19 posts
Defender XDR
ISOC Is a Licence Change in an Agentic Costume (And That's Actually Good News)
All right class.
You've got E5. You've got Defender filling the incident queue before your first coffee. You haven't got Sentinel, because
 Career Advice
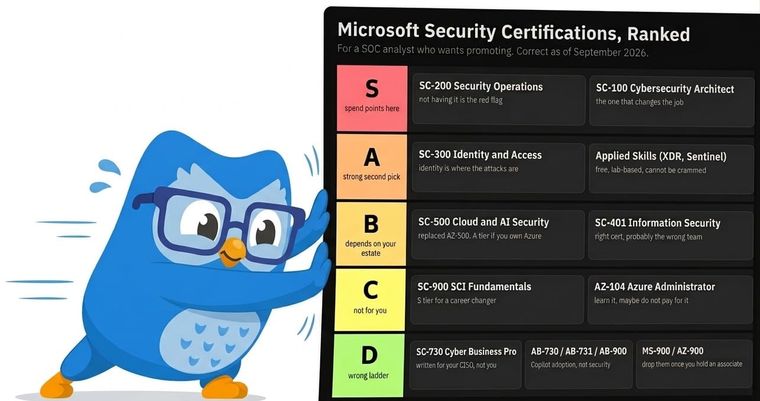
Microsoft Security Certifications, Ranked: What Actually Moves You Up
All right class.
You're in a SOC. You've been triaging incidents for two years, you're good at it, and you've
 Defender XDR
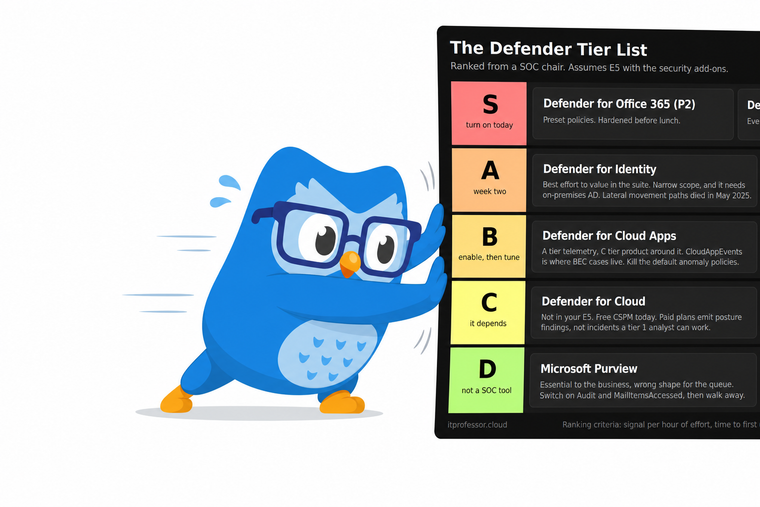
The Defender Tier List: What to Turn On First When You Own All of It
All right class.
You have E5. Every Defender product in the suite is licensed and sitting there. Somebody enabled Defender for Endpoint on about two thirds of the
 Defender XDR
You're Paying for Defender XDR Features You Never Enabled
All right class.
You got yourself a good little E5 license. Defender is onboarded. You've got incidents firing, KQL running, analysts investigating. Job done, right?
Go
 Detection Engineering
Is Your SOC Actually Doing Anything? Here Is How to Find Out
All right class.
A friend of mine recently took over a security engineering position. The company had a managed SOC on a five year contract, three years into
 Microsoft Sentinel
Choosing a Microsoft MSSP Without Getting Burned (SOC/SIEM)
All right class.
Too many companies hand their entire security operation to the first provider who can say "Sentinel" without choking. Six months later, the invoices
 Detection Engineering
 and Why It's a Must Have Part 2
All right class
This is a continuation of part 1 that you can find here.
Detection Engineering: Why Your SIEM Won’t Save YouDetection engineering bridges the gap
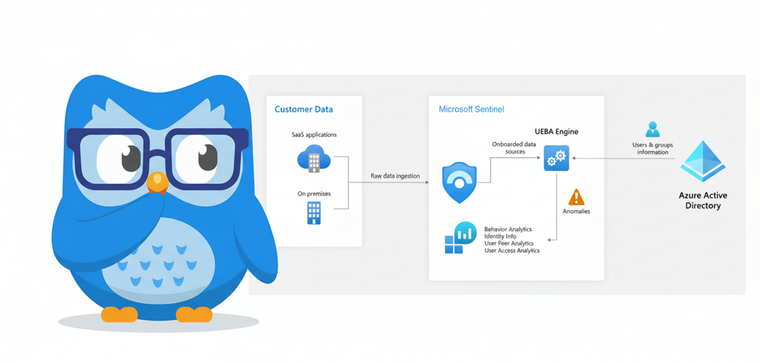 Microsoft Sentinel
UEBA in Microsoft Sentinel: Stop Wasting Time on Behavioral Analytics
Welcome back, class.
You've probably heard the pitch: enable UEBA, and anomalies magically surface threats. Your analysts get smarter. False positives drop. Insider threats get caught.
 Security Operations
Connecting Your Environment to Defender for Cloud: Azure, AWS, GCP, and On-Premises
Alright, class. You've decided to actually use Defender for Cloud. Now comes the fun part: connecting everything.
Your infrastructure is scattered. Azure here. AWS there. Some
 SOC
Why You Actually Need Microsoft Defender for Cloud (And What It Actually Does)
Alright, class. Take your seats.
Your infrastructure is in the cloud now. Could be Azure. Might be AWS. Probably both. Maybe GCP too, because apparently someone in your
 Microsoft Defender for Cloud Apps
App Governance in Defender for Cloud Apps: Your OAuth App Security Command Centre
Alright, class. Take your seats.
We've covered Shadow IT discovery. We've drilled deep into policies. You've learned how to detect, block, and
 Microsoft Defender for Cloud Apps
Mastering Policies in Defender for Cloud Apps: A Deep Dive for the SOC Trenches
Alright, class. Take your seats. Today is a long lesson, but given the subject, it's well worth it. Grab your coffee (and maybe another one down

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.