 KQL
Would You Know If Someone Cancelled Your Azure Subscription?
Alright class.
Yet another lesson in this series, and this one breaks the format. There is no Microsoft rule to fix today, because Microsoft does not ship one.
Topic
Detection Engineering
Detection engineering for Microsoft Sentinel and Defender XDR: building, testing and rebuilding analytic rules so they catch attacks instead of noise.
35 posts
KQL
Would You Know If Someone Cancelled Your Azure Subscription?
Alright class.
Yet another lesson in this series, and this one breaks the format. There is no Microsoft rule to fix today, because Microsoft does not ship one.
 Microsoft Sentinel
Fixing the "Application URL" Analytic Rules, All Three of Them
Alright class.
Another lesson, first one fixing three rules at once. The content hub ships "Changes to Application Logout URL", "Application Redirect URL Update"
 KQL
Fixing the "Guest Users Invited to Tenant by New Inviters" Analytic Rule
Alright class.
Today we are looking at "Guest Users Invited to Tenant by New Inviters", a content hub rule that promises to spot guest account abuse
 Microsoft Sentinel
Anyone With the Link
All right class.
Somebody shared a file this week by picking the option at the top of the list. The one that says Anyone with the link. It
 KQL
The Antivirus Setting Your Admins Turned Off Years Ago
All right class.
Somewhere in your estate there is a device with C:\ in its Defender exclusion list. Somebody put it there in 2021 to stop a line
 KQL
Fixing the "Excessive Windows Logon Failures" Analytic Rule
Alright class.
A close cousin to one of the previous lessons - that rule counted failures in a 10 minute burst. This one takes a whole day and tries
 Microsoft Sentinel
Fixing the "Failed Logon Attempts by Valid Accounts within 10 mins" Analytic Rule
Alright class.
On-premises this time, back in the Windows security log. The rule watches event 4625, a failed logon, and fires when a valid account fails 20
 Microsoft Sentinel
Fixing the "Microsoft Entra ID PowerShell accessing non-Entra ID resources" Analytic Rule
Alright class.
Today's rule is "Microsoft Entra ID PowerShell accessing non-Entra ID resources", which alerts when the old Azure AD PowerShell client obtains
 Microsoft Sentinel
Fixing the "Mass Cloud resource deletions Time Series Anomaly" Analytic Rule
Alright class.
Today we are looking at Mass Cloud resource deletions Time Series Anomaly, a content hub rule that promises to catch an adversary tearing down your Azure
 KQL
Fixing the "Suspicious granting of permissions to an account" Analytic Rule
Alright class.
Today's patient is "Suspicious granting of permissions to an account", the content hub rule that promises an alert "when a previously
 Microsoft Sentinel
Fixing the "Rare Subscription-level Operations in Azure" Analytic Rule
Alright class.
Back on the Azure control plane, and a rule with a good nose for targets. It watches AzureActivity for sensitive subscription operations, and the description picks
 Career Advice
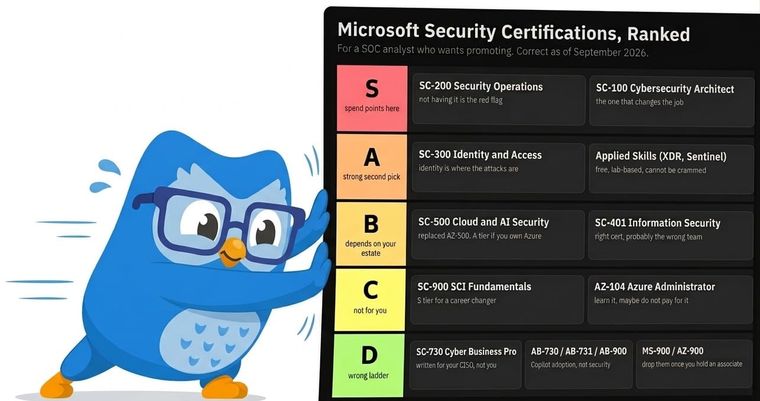
Microsoft Security Certifications, Ranked: What Actually Moves You Up
All right class.
You're in a SOC. You've been triaging incidents for two years, you're good at it, and you've
Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.