 Microsoft Sentinel
Fixing the "Mass Cloud resource deletions Time Series Anomaly" Analytic Rule
Alright class.
Today we are looking at Mass Cloud resource deletions Time Series Anomaly, a content hub rule that promises to catch an adversary tearing down your Azure
Author
Bartosz Wysocki
Head of security engineering at a UK MSSP. I started as a SOC analyst and never stopped writing KQL. These days I build the detections, automation and reporting behind a managed SOC on Sentinel and Defender. Profo does the drawings.
121 posts
Microsoft Sentinel
Fixing the "Mass Cloud resource deletions Time Series Anomaly" Analytic Rule
Alright class.
Today we are looking at Mass Cloud resource deletions Time Series Anomaly, a content hub rule that promises to catch an adversary tearing down your Azure
 KQL
Fixing the "Suspicious granting of permissions to an account" Analytic Rule
Alright class.
Today's patient is "Suspicious granting of permissions to an account", the content hub rule that promises an alert "when a previously
 Microsoft Defender for Cloud Apps
The Defender Indicators Page Nobody Opens (But Every SOC Should)
All right class.
There is a page in the Defender portal you have almost certainly never opened. It sits at Settings > Endpoints > Indicators, tucked under Rules,
 KQL
Conditional Access, Part Six: Turning Twenty-Five Queries Into an Operating Model
All right class.
Five posts, twenty-five queries. If you have been following along, you now have a folder of KQL that describes your Conditional Access estate better
 Microsoft Sentinel
Fixing the "Rare Subscription-level Operations in Azure" Analytic Rule
Alright class.
Back on the Azure control plane, and a rule with a good nose for targets. It watches AzureActivity for sensitive subscription operations, and the description picks
 KQL
Conditional Access, Part Five: Cross-Tenant Access, MFA Trust, and the Partner Problem
All right class.
Part two left a loose end and I promised to come back for it. Guests cannot register passkeys in your tenant (MC1459133 starts fixing this
 Entra ID
Conditional Access, Part Four: Tokens, Sessions, and the Control You Do Not Have
All right class.
Three posts in. We designed the estate, we fixed the credential, and we dealt with the device. Every one of those controls does its work
 Career Advice
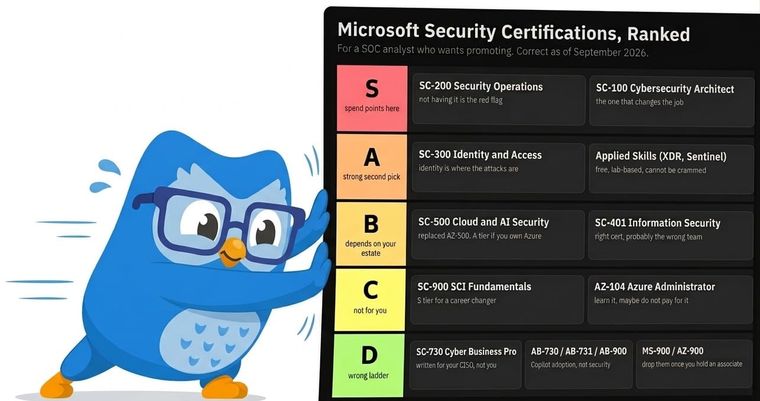
Microsoft Security Certifications, Ranked: What Actually Moves You Up
All right class.
You're in a SOC. You've been triaging incidents for two years, you're good at it, and you've
 Microsoft Sentinel
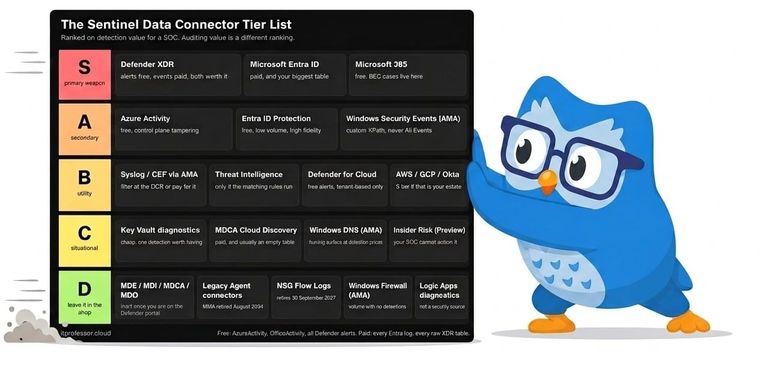
The Sentinel Data Connector Tier List: What Earns a Slot in Your Loadout
All right class.
The Content Hub is a shop with hundreds of items and no gold limit. Every connector is right there, every one of them is free
 Defender XDR
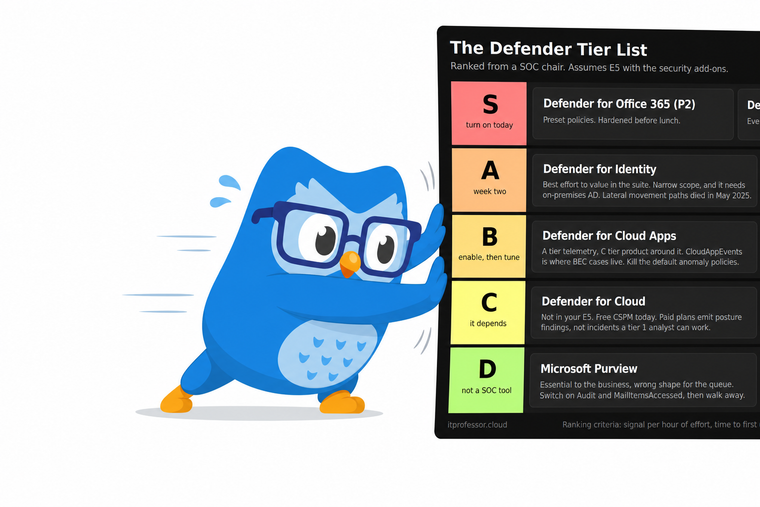
The Defender Tier List: What to Turn On First When You Own All of It
All right class.
You have E5. Every Defender product in the suite is licensed and sitting there. Somebody enabled Defender for Endpoint on about two thirds of the
 KQL
Conditional Access, Part Three: Device Controls, and What Compliant Actually Proves
All right class.
Two posts in. We built the estate, and then we fixed the credential. Today we deal with the control that most security teams rate as
 Conditional Access
, Part Two: Authentication Strengths and the Road to Phishing-Resistant
All right class.
Conditional Access, Part One: Design the EstatePart one of the series covers how the engine actually decides, the persona model, naming, exclusions, ring deployment, the
Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.