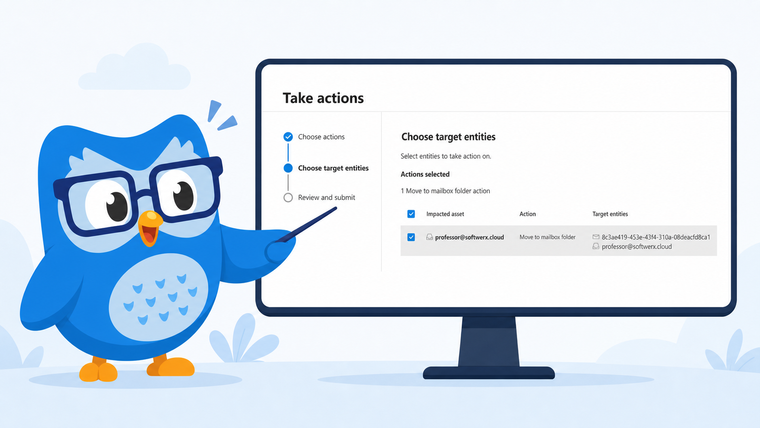
 Advanced Hunting
 Just Got a Lot More Powerful. You Can Now Act on What You Find.
All right class
Hunting was always "find bad things and tell someone".
You'd write your KQL, find the compromised devices, copy a list of
Topic
Incident Response
Incident response in Microsoft Sentinel and Defender XDR: investigating incidents, containment, response actions, threat intel and custom detections.
7 posts
Advanced Hunting
Advanced Hunting Just Got a Lot More Powerful. You Can Now Act on What You Find.
All right class
Hunting was always "find bad things and tell someone".
You'd write your KQL, find the compromised devices, copy a list of
 Microsoft Sentinel
The Nag Machine: A Logic App That Badgers Your Team About Unowned Sentinel Incidents
All right class
Today is a quick one so you can enjoy deploying it without reading a whole lot about this.
The idea is simple - you are getting
 Defender XDR
 Incident Investigation: A to Z Using a Real Example
All right class.
There are a few ways you end up staring at an incident queue with no idea what to do with it.
Operation Silent Ledger: SOC
 Microsoft Sentinel
Beyond the Basics: Forging Your Own Custom Detections in Defender XDR
Alright, class.
You've started to notice something. Sentinel is the brilliant general in the command tent, seeing the whole battlefield. The actual guards on the walls,
 Microsoft Sentinel
Hunting Ransomware in Storage Accounts (When You Can't Afford Defender)
Alright, class.
Let's talk about the crown jewels of your Azure kingdom: your Storage Accounts. It's where you keep your critical application data, your
 Microsoft Sentinel
Microsoft Threat Intelligence: Giving Your Sentinel a Brain
Alright, class.
Let's talk about the first question every SOC analyst asks when a new alert fires. You see an incident for a strange sign-in
 Microsoft Sentinel
: An Incident Just Fired. Now What? (A Beginner's Guide to Investigation)
Welcome back to the command centre, class. So far, you've deployed Sentinel, connected your data, and built your first Analytic Rule. You've essentially set

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.