 KQL
The Antivirus Setting Your Admins Turned Off Years Ago
All right class.
Somewhere in your estate there is a device with C:\ in its Defender exclusion list. Somebody put it there in 2021 to stop a line
Topic
Defender XDR
Microsoft Defender XDR from the SOC chair: settings worth turning on, incident investigation, Threat Analytics, critical assets and what to enable first.
15 posts
KQL
The Antivirus Setting Your Admins Turned Off Years Ago
All right class.
Somewhere in your estate there is a device with C:\ in its Defender exclusion list. Somebody put it there in 2021 to stop a line
 Microsoft Sentinel
The Sentinel Data Lake Got Respecced: What Actually Moved to Fabric
All right class.
You moved your firewall logs to the data lake tier because the analytics bill had turned into a monthly argument with finance. You built a
 Defender XDR
ISOC Is a Licence Change in an Agentic Costume (And That's Actually Good News)
All right class.
You've got E5. You've got Defender filling the incident queue before your first coffee. You haven't got Sentinel, because
 Microsoft Defender for Cloud Apps
The Defender Indicators Page Nobody Opens (But Every SOC Should)
All right class.
There is a page in the Defender portal you have almost certainly never opened. It sits at Settings > Endpoints > Indicators, tucked under Rules,
 Defender XDR
The Defender Tier List: What to Turn On First When You Own All of It
All right class.
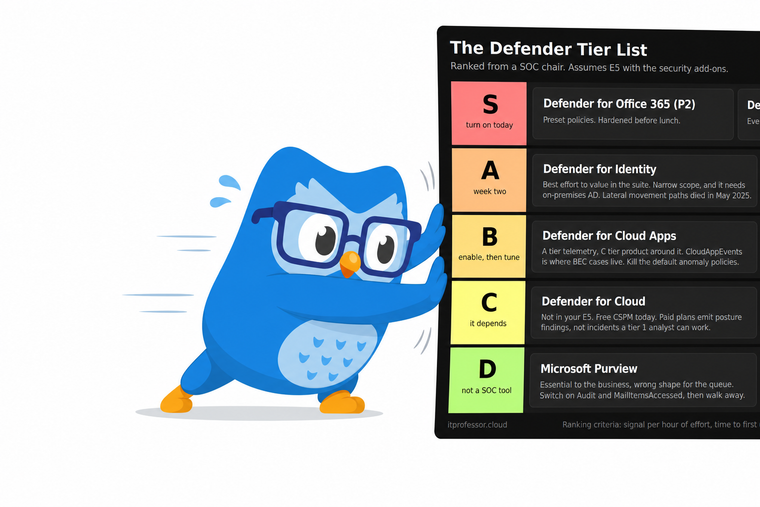
You have E5. Every Defender product in the suite is licensed and sitting there. Somebody enabled Defender for Endpoint on about two thirds of the
 Microsoft Defender for Cloud Apps
Defender for Cloud Apps Settings You've Never Touched (But Should)
All right class.
You have Defender for Cloud Apps in your E5 licence. You logged into it once, looked at the Cloud Discovery dashboard, felt impressed with yourself,
 Defender XDR
You're Paying for Defender XDR Features You Never Enabled
All right class.
You got yourself a good little E5 license. Defender is onboarded. You've got incidents firing, KQL running, analysts investigating. Job done, right?
Go
 Advanced Hunting
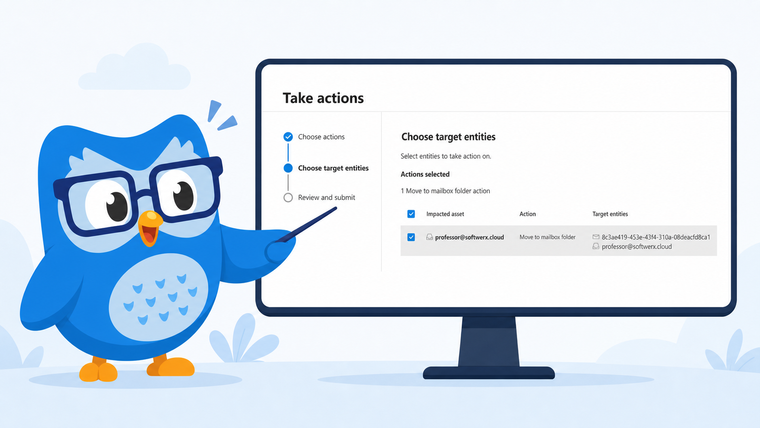
 Just Got a Lot More Powerful. You Can Now Act on What You Find.
All right class
Hunting was always "find bad things and tell someone".
You'd write your KQL, find the compromised devices, copy a list of
 Defender XDR
Your Crown Jewels Are in Defender. You Just Never Set Them Up.
All right class.
You have been saying "crown jewels" and "tier zero assets" in meetings for years. You can explain exactly why domain controllers
 Defender XDR
 Incident Investigation: A to Z Using a Real Example
All right class.
There are a few ways you end up staring at an incident queue with no idea what to do with it.
Operation Silent Ledger: SOC
 Defender XDR
Defender for Identity: What's The Point? (And Is It Actually Worth Your Time)
All right class.
You have Active Directory. You have domain controllers. You're probably already paying for M365 or E5. Microsoft ships Defender for Identity and tells
 Microsoft Sentinel
Data Connectors: The Order That Actually Matters
All right class
I've seen people enable data connectors wrong. They grab whatever sounds useful, flip the switch, and hope detection happens. You need a sequence.

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.