 Defender XDR
ISOC Is a Licence Change in an Agentic Costume (And That's Actually Good News)
All right class.
You've got E5. You've got Defender filling the incident queue before your first coffee. You haven't got Sentinel, because
Topic
SOC
For SOC analysts on the Microsoft stack: triage, investigations, hunting, interviews and the day-to-day work in Sentinel and Defender nobody teaches.
37 posts
Defender XDR
ISOC Is a Licence Change in an Agentic Costume (And That's Actually Good News)
All right class.
You've got E5. You've got Defender filling the incident queue before your first coffee. You haven't got Sentinel, because
 Career Advice
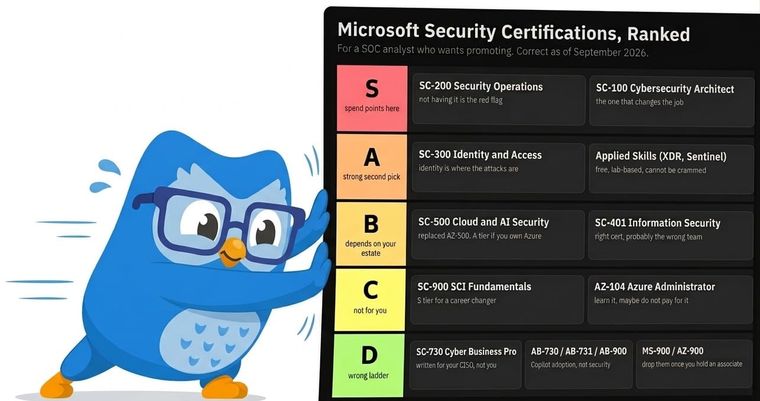
Microsoft Security Certifications, Ranked: What Actually Moves You Up
All right class.
You're in a SOC. You've been triaging incidents for two years, you're good at it, and you've
 Microsoft Sentinel
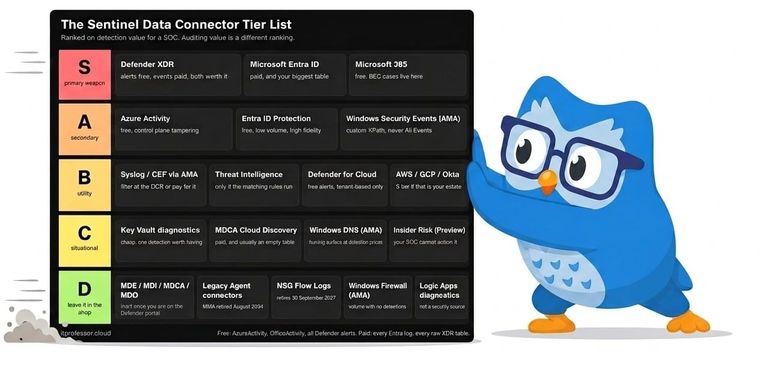
The Sentinel Data Connector Tier List: What Earns a Slot in Your Loadout
All right class.
The Content Hub is a shop with hundreds of items and no gold limit. Every connector is right there, every one of them is free
 Defender XDR
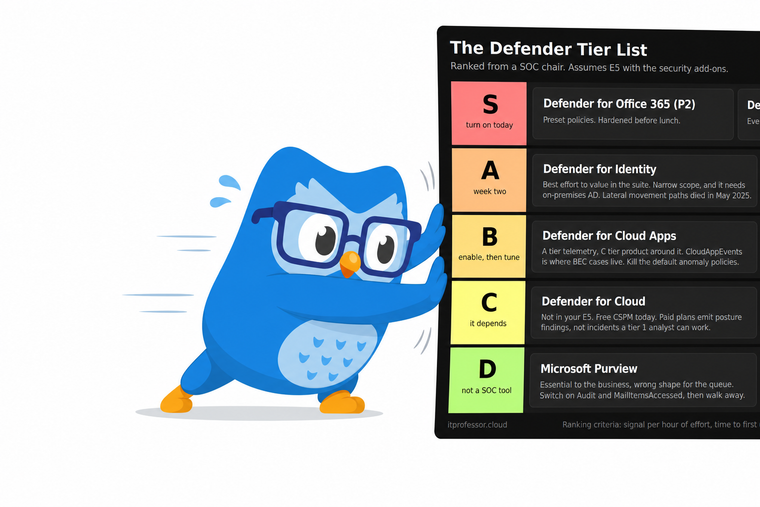
The Defender Tier List: What to Turn On First When You Own All of It
All right class.
You have E5. Every Defender product in the suite is licensed and sitting there. Somebody enabled Defender for Endpoint on about two thirds of the
 Microsoft Defender for Cloud Apps
Defender for Cloud Apps Settings You've Never Touched (But Should)
All right class.
You have Defender for Cloud Apps in your E5 licence. You logged into it once, looked at the Cloud Discovery dashboard, felt impressed with yourself,
 Defender XDR
You're Paying for Defender XDR Features You Never Enabled
All right class.
You got yourself a good little E5 license. Defender is onboarded. You've got incidents firing, KQL running, analysts investigating. Job done, right?
Go
 Detection Engineering
Is Your SOC Actually Doing Anything? Here Is How to Find Out
All right class.
A friend of mine recently took over a security engineering position. The company had a managed SOC on a five year contract, three years into
 SOC
Evaluating and Onboarding a Microsoft MSSP (Without the Chaos)
All right class
If you read lesson one, you already know how to define your scope, lock down your log retention, and write an RFP that forces vendors
 Microsoft Sentinel
Detection Engineering and Why It's a Must Have
Why Your SIEM Won't Save You Without It
All right class
I've seen people think that you can just turn on Microsoft Sentinel, wiring
 Defender XDR
Defender for Identity: What's The Point? (And Is It Actually Worth Your Time)
All right class.
You have Active Directory. You have domain controllers. You're probably already paying for M365 or E5. Microsoft ships Defender for Identity and tells
 Microsoft Sentinel
 on a Shoestring: What You Can Actually Do with Business Premium
All right class
You have Entra ID P1 and Business Premium. You need a SIEM. This is what you can actually build, what it costs, and how to
 SOC
KQL User Audit Playbook V2: The Insider Threat Investigation Guide
All right class.
This is a continuation of my previous lesson, which contains useful queries for insider risk hunting. Make sure to read it first, as it may

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.