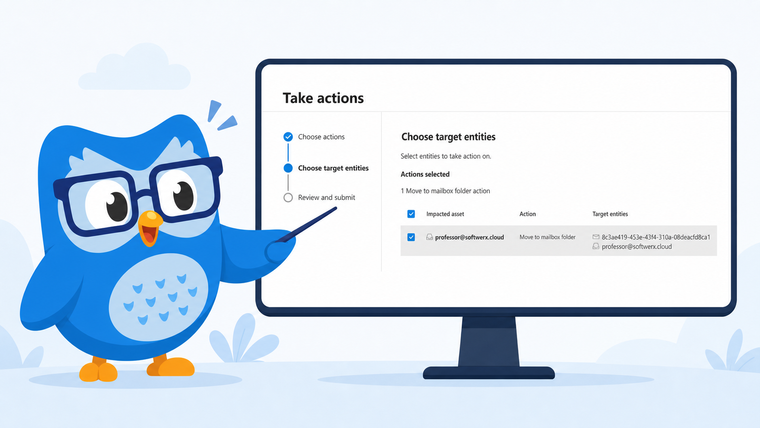
 Advanced Hunting
 Just Got a Lot More Powerful. You Can Now Act on What You Find.
All right class
Hunting was always "find bad things and tell someone".
You'd write your KQL, find the compromised devices, copy a list of
Author
Bartosz Wysocki
Head of security engineering at a UK MSSP. I started as a SOC analyst and never stopped writing KQL. These days I build the detections, automation and reporting behind a managed SOC on Sentinel and Defender. Profo does the drawings.
121 posts
Advanced Hunting
Advanced Hunting Just Got a Lot More Powerful. You Can Now Act on What You Find.
All right class
Hunting was always "find bad things and tell someone".
You'd write your KQL, find the compromised devices, copy a list of
 Microsoft Sentinel
The Nag Machine: A Logic App That Badgers Your Team About Unowned Sentinel Incidents
All right class
Today is a quick one so you can enjoy deploying it without reading a whole lot about this.
The idea is simple - you are getting
 Defender XDR
Your Crown Jewels Are in Defender. You Just Never Set Them Up.
All right class.
You have been saying "crown jewels" and "tier zero assets" in meetings for years. You can explain exactly why domain controllers
 Threat Hunting
Building Your First Threat Hunting Hypothesis (The MITRE Way)
All right class.
Lots of SOC teams say they do threat hunting. What they actually do is run a couple of saved KQL queries on a Friday afternoon
 Microsoft Sentinel
Diagnostic Settings Manager Workbook
All right class
This one is free to grab. No strings attached.
Getting resources into Sentinel is one of those tasks that sounds simple until you're
 Microsoft Sentinel
Azure Key Vault: The High-Value Queries Your SOC Isn't Running
All right class.
Key Vault is where your secrets live. Connection strings, API keys, certificates, encryption keys, service account credentials. If an attacker gets into your environment and
 KQL
Hunting PowerShell Abuse in MDE: Eight Queries, Real Results
All right class
PowerShell is in every serious Windows intrusion. Not because attackers are creative, but because it works, it's already there, and it leaves just
 Detection Engineering
I Passed the GCDA. Here's What Nobody Tells You About SEC555
All right class.
Three months of preparation, five books read twice, a physical index that grew to four pages, and an exam experience that reminded me why I
 Microsoft Sentinel
Your Sentinel Detection Setup Is Probably Broken. Here's How to Know.
All right class
Most environments running Sentinel today have the same problem. The toggle is on. Rules are firing. UEBA is enabled. And nobody trusts any of it.
 Defender XDR
 Incident Investigation: A to Z Using a Real Example
All right class.
There are a few ways you end up staring at an incident queue with no idea what to do with it.
Operation Silent Ledger: SOC
 SOC
Evaluating and Onboarding a Microsoft MSSP (Without the Chaos)
All right class
If you read lesson one, you already know how to define your scope, lock down your log retention, and write an RFP that forces vendors
 Microsoft Sentinel
Choosing a Microsoft MSSP Without Getting Burned (SOC/SIEM)
All right class.
Too many companies hand their entire security operation to the first provider who can say "Sentinel" without choking. Six months later, the invoices
Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.