 Microsoft Sentinel
Teams Threat Protection: What Actually Changed and What You Can Actually Hunt
All right class
Your SOC has limited visibility into Teams. Attackers run credential theft campaigns in chat. You see some of it through audit logs if you'
Topic
SOC
For SOC analysts on the Microsoft stack: triage, investigations, hunting, interviews and the day-to-day work in Sentinel and Defender nobody teaches.
37 posts
Microsoft Sentinel
Teams Threat Protection: What Actually Changed and What You Can Actually Hunt
All right class
Your SOC has limited visibility into Teams. Attackers run credential theft campaigns in chat. You see some of it through audit logs if you'
 SOC
Threat Analytics in Microsoft Defender: What It Actually Does and Why Your SOC Needs It
All right class.
You're doing your SOC investigations at 3 pm Tuesday. A threat report drops that a Chinese state-backed group is hitting financial services
 SOC
Hunting in Microsoft Sentinel: What Hunting Actually Is and Why You Need It
Terminology matters here. Microsoft uses these words in specific ways, and if you get them wrong, you'll waste time doing the wrong thing.
What Is Hunting
 Sentinel Workbook
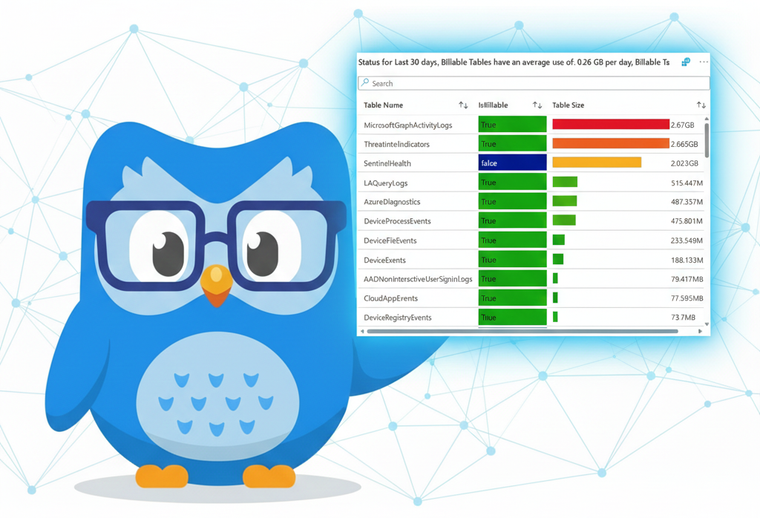
Three Essential Sentinel Workbooks You Should Deploy Right Now
All right class.
Workbooks That Actually Solve Problems
Microsoft has already built three workbooks in Content Hub that handle the problems you're dealing with right now.
 Microsoft Sentinel
Sentinel Workbooks: Deploy and Customise Your First Dashboard
Welcome back class.
You're running Sentinel. Logs are flowing. Alerts are firing. And your team is copy-pasting the same KQL query into Log Analytics fifty
 KQL
Beauty of Data Visualization in Microsoft Sentinel Using KQL
Welcome back, class.
Tables are useless at scale. You know this already. A thousand rows of sign-in data tell you nothing. A hundred thousand rows of process
 Defender XDR
Defender for Office 365 Policy Configuration: Anti-Phishing, Anti-Spam, Malware, Safe Links
All right class.
Microsoft's preset policies are marketing fiction. They sound good in documentation. In production? The standard may be too permissive and miss sophisticated attacks.
 Microsoft Sentinel
Is Defender for Office 365 worth it?
All right class.
Your email is already protected by Exchange Online Protection. So why would you pay for Defender for Office 365 on top of that?
That'
 Microsoft Sentinel
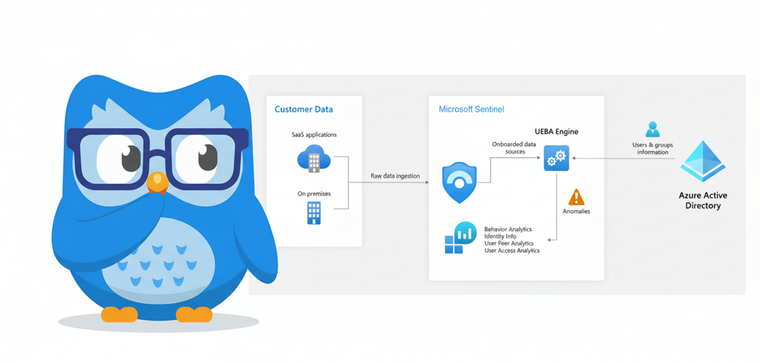
UEBA in Microsoft Sentinel: Stop Wasting Time on Behavioral Analytics
Welcome back, class.
You've probably heard the pitch: enable UEBA, and anomalies magically surface threats. Your analysts get smarter. False positives drop. Insider threats get caught.
 KQL
Building a Brute Force Detection Query: How To Think Through Network Logon Failures
All right class, take your seats.
This post is about methodology. How do you go from "I want to hunt brute force attempts" to a query
 SOC
Attack Simulation Training in Microsoft Defender for Office 365
Allright class
Built into your Microsoft 365 E5 or Defender for Office 365 Plan 2 license is a phishing simulation tool that doesn't suck as hard
 Microsoft Sentinel
Continuous Export to Log Analytics: Getting Defender for Cloud Data Where You Need It
Alright, class.
You've got Defender for Cloud on. Alerts keep firing. Recommendations keep stacking. Your Secure Score bounces around daily. The problem is all of it

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.