 KQL
Sentinel Table Transformations: Cut the Table, Keep the Detections
All right class
Two lessons ago we found the spike.
Here you learned how to walk the Usage table backwards until your data confesses.
Sentinel Log Spikes: Find
Topic
Cost Optimisation
Cut your Microsoft Sentinel bill without losing detections: ingestion spikes, table tiers, transformations, the data lake and what to stop collecting.
15 posts
KQL
Sentinel Table Transformations: Cut the Table, Keep the Detections
All right class
Two lessons ago we found the spike.
Here you learned how to walk the Usage table backwards until your data confesses.
Sentinel Log Spikes: Find
 Microsoft Sentinel
The Sentinel Data Lake Got Respecced: What Actually Moved to Fabric
All right class.
You moved your firewall logs to the data lake tier because the analytics bill had turned into a monthly argument with finance. You built a
 Defender XDR
ISOC Is a Licence Change in an Agentic Costume (And That's Actually Good News)
All right class.
You've got E5. You've got Defender filling the incident queue before your first coffee. You haven't got Sentinel, because
 Microsoft Sentinel
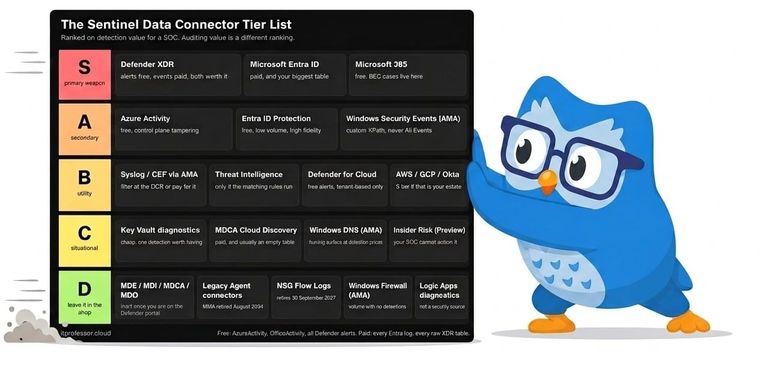
The Sentinel Data Connector Tier List: What Earns a Slot in Your Loadout
All right class.
The Content Hub is a shop with hundreds of items and no gold limit. Every connector is right there, every one of them is free
 Defender XDR
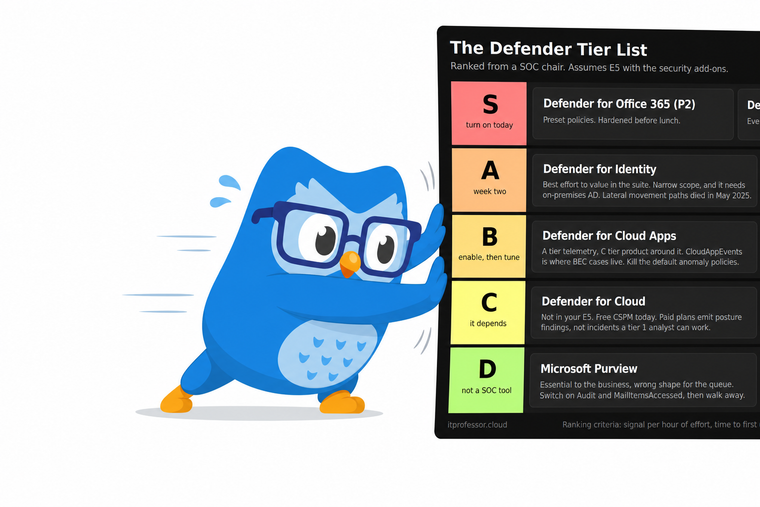
The Defender Tier List: What to Turn On First When You Own All of It
All right class.
You have E5. Every Defender product in the suite is licensed and sitting there. Somebody enabled Defender for Endpoint on about two thirds of the
 Microsoft Sentinel
Every Microsoft Sentinel Content Hub Rule for Business Premium: What to Enable, Auto-Close, and Skip
All right class.
If you have not read the original post yet, start there. This one assumes you already have Sentinel running with Entra ID, Defender alerts, Azure
 Sentinel Workbook
Why Abandoned Resources Are a Security Problem, Not Just a Billing One
Everything here is built on the work of Dolev Shor. His Azure Orphaned Resources workbook has 745 GitHub stars and is genuinely one of the most useful things
 Microsoft Sentinel
Sentinel Cost Spike: How To Actually Find The Culprit Table
All right class.
Your CFO walks over and asks why the Azure bill just went up and why “Microsoft Sentinel” is suddenly the top line item.
You open
 Microsoft Sentinel
 on a Shoestring: What You Can Actually Do with Business Premium
All right class
You have Entra ID P1 and Business Premium. You need a SIEM. This is what you can actually build, what it costs, and how to
 Microsoft Sentinel
Sentinel Deployment Checklist: What You Actually Need Before Day One
All right class.
This is the pre-deployment checklist for people who actually want to know what they're doing. The architectural decisions that determine whether you
 Microsoft Sentinel
Post-Deployment Sentinel and Defender XDR: You're Not Done Yet
Alright, class.
So you've deployed Sentinel. You've got Defender XDR running. Your SOC is live. Alerts are coming in. Your Secure Score went up.
 Microsoft Sentinel
The "Undo" Button for Sentinel Logs: An In-Depth Guide to Purging Data
Alright, class.
Let's talk about the "I have made a terrible, expensive mistake" moment.
You just onboarded a new data source. You thought you

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.