 KQL
Fixing the "Rare Application Consent" Analytic Rule
Alright class.
Back in the Entra audit log for this one. The rule is called "Rare application consent" and the premise comes straight from consent phishing:
Topic
Detection Engineering
Detection engineering for Microsoft Sentinel and Defender XDR: building, testing and rebuilding analytic rules so they catch attacks instead of noise.
35 posts
KQL
Fixing the "Rare Application Consent" Analytic Rule
Alright class.
Back in the Entra audit log for this one. The rule is called "Rare application consent" and the premise comes straight from consent phishing:
 Microsoft Sentinel
Fixing the "Account Created From Non-Approved Sources" Analytic Rule
Alright class.
A companion piece to the last lesson, from the same Microsoft security-operations page. This one is "Account created from non-approved sources": it
 Microsoft Sentinel
Fixing the "Account Created or Deleted by Non-Approved User" Analytic Rule
Alright class.
This one comes from the Entra ID audit log, and it is the strangest thing Microsoft ships in the content hub. It is called "Account
 Microsoft Sentinel
Fixing the "Account Created and Deleted in Short Timeframe" Analytic Rule
Alright class.
Today it is "Account Created and Deleted in Short Timeframe". The rule pairs a "Delete user" event with an earlier "Add
 Detection Engineering
Is Your SOC Actually Doing Anything? Here Is How to Find Out
All right class.
A friend of mine recently took over a security engineering position. The company had a managed SOC on a five year contract, three years into
 Microsoft Sentinel
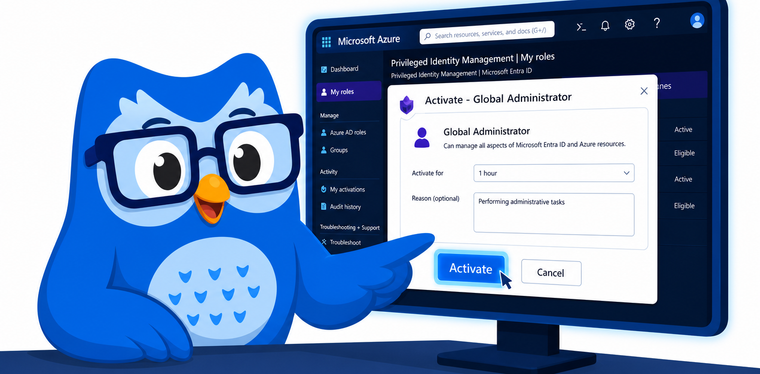
PIM Auditing in Microsoft Sentinel: High Value Detections
Alright class.
Most lessons in this series are usually autopsies. We take a content hub rule, find the line that breaks it, and put it back together properly.
 Defender XDR
Your Crown Jewels Are in Defender. You Just Never Set Them Up.
All right class.
You have been saying "crown jewels" and "tier zero assets" in meetings for years. You can explain exactly why domain controllers
 Detection Engineering
I Passed the GCDA. Here's What Nobody Tells You About SEC555
All right class.
Three months of preparation, five books read twice, a physical index that grew to four pages, and an exam experience that reminded me why I
 Microsoft Sentinel
Your Sentinel Detection Setup Is Probably Broken. Here's How to Know.
All right class
Most environments running Sentinel today have the same problem. The toggle is on. Rules are firing. UEBA is enabled. And nobody trusts any of it.
 Detection Engineering
 and Why It's a Must Have Part 2
All right class
This is a continuation of part 1 that you can find here.
Detection Engineering: Why Your SIEM Won’t Save YouDetection engineering bridges the gap
 Microsoft Sentinel
Detection Engineering and Why It's a Must Have
Why Your SIEM Won't Save You Without It
All right class
I've seen people think that you can just turn on Microsoft Sentinel, wiring
Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.