 KQL
The Guests Who Never Left
All right class.
Every tenant has them. A guest invited in 2019 for a migration project that finished in 2020, invited by somebody who left in 2022, still
Topic
Advanced Hunting
Advanced Hunting in Microsoft Defender XDR: KQL queries, response actions straight from results, and audits you can run against your own tenant today.
6 posts
KQL
The Guests Who Never Left
All right class.
Every tenant has them. A guest invited in 2019 for a migration project that finished in 2020, invited by somebody who left in 2022, still
 KQL
The Antivirus Setting Your Admins Turned Off Years Ago
All right class.
Somewhere in your estate there is a device with C:\ in its Defender exclusion list. Somebody put it there in 2021 to stop a line
 KQL
Operation Silent Ledger: A SOC Tabletop Exercise for Adversary in the Middle Phishing
Alright class.
Every tabletop exercise I have sat in ended with everybody agreeing on the right answer. That is the problem with them. There is no clock in
 Advanced Hunting
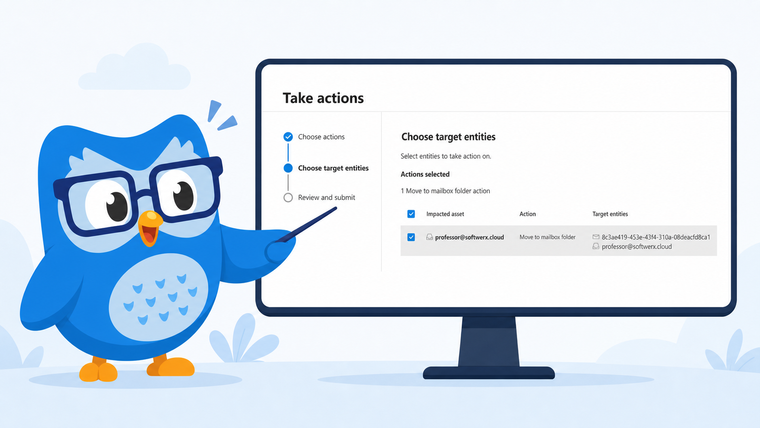
 Just Got a Lot More Powerful. You Can Now Act on What You Find.
All right class
Hunting was always "find bad things and tell someone".
You'd write your KQL, find the compromised devices, copy a list of
 Defender XDR
 Incident Investigation: A to Z Using a Real Example
All right class.
There are a few ways you end up staring at an incident queue with no idea what to do with it.
Operation Silent Ledger: SOC
 KQL
Building a Brute Force Detection Query: How To Think Through Network Logon Failures
All right class, take your seats.
This post is about methodology. How do you go from "I want to hunt brute force attempts" to a query

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.