 KQL
Beauty of Data Visualization in Microsoft Sentinel Using KQL
Welcome back, class.
Tables are useless at scale. You know this already. A thousand rows of sign-in data tell you nothing. A hundred thousand rows of process
Topic
Microsoft Sentinel
Practical Microsoft Sentinel guides from someone running it in production: deployment, connectors, analytic rules, cost control and investigations.
97 posts
KQL
Beauty of Data Visualization in Microsoft Sentinel Using KQL
Welcome back, class.
Tables are useless at scale. You know this already. A thousand rows of sign-in data tell you nothing. A hundred thousand rows of process
 Defender XDR
Defender for Office 365 Policy Configuration: Anti-Phishing, Anti-Spam, Malware, Safe Links
All right class.
Microsoft's preset policies are marketing fiction. They sound good in documentation. In production? The standard may be too permissive and miss sophisticated attacks.
 Microsoft Sentinel
Is Defender for Office 365 worth it?
All right class.
Your email is already protected by Exchange Online Protection. So why would you pay for Defender for Office 365 on top of that?
That'
 Microsoft Sentinel
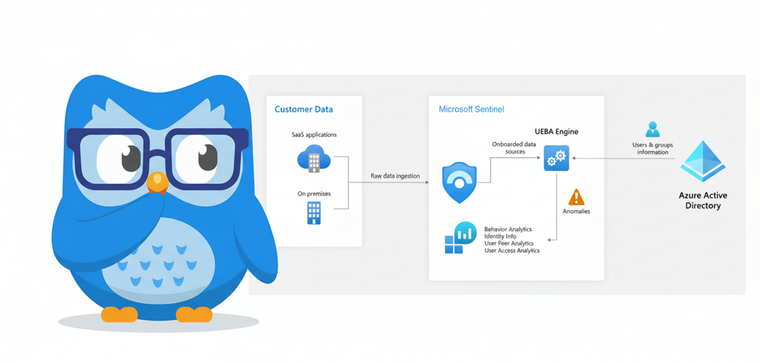
UEBA in Microsoft Sentinel: Stop Wasting Time on Behavioral Analytics
Welcome back, class.
You've probably heard the pitch: enable UEBA, and anomalies magically surface threats. Your analysts get smarter. False positives drop. Insider threats get caught.
 KQL
Fixing Microsoft's Azure Brute Force Detection: Why Their Template Fires Constantly (And What You Should Change)
All right class.
Microsoft ships an out-of-the-box analytic rule for Azure Portal brute force attempts. It looks good on paper. It catches failures. It'
 KQL
Building a Brute Force Detection Query: How To Think Through Network Logon Failures
All right class, take your seats.
This post is about methodology. How do you go from "I want to hunt brute force attempts" to a query
 Microsoft Sentinel
Continuous Export to Log Analytics: Getting Defender for Cloud Data Where You Need It
Alright, class.
You've got Defender for Cloud on. Alerts keep firing. Recommendations keep stacking. Your Secure Score bounces around daily. The problem is all of it
 Microsoft Sentinel
Post-Deployment Sentinel and Defender XDR: You're Not Done Yet
Alright, class.
So you've deployed Sentinel. You've got Defender XDR running. Your SOC is live. Alerts are coming in. Your Secure Score went up.
 Microsoft Defender for Cloud Apps
App Governance in Defender for Cloud Apps: Your OAuth App Security Command Centre
Alright, class. Take your seats.
We've covered Shadow IT discovery. We've drilled deep into policies. You've learned how to detect, block, and
 Microsoft Defender for Cloud Apps
Mastering Policies in Defender for Cloud Apps: A Deep Dive for the SOC Trenches
Alright, class. Take your seats. Today is a long lesson, but given the subject, it's well worth it. Grab your coffee (and maybe another one down
 Microsoft Defender for Cloud Apps
A SOC Analyst's Introduction to Defender for Cloud Apps
Alright, class. Take your seats.
Let's talk about a problem that keeps every security professional up at night. It's not the alerts you see;
 KQL
The KQL User Audit Playbook: Your Template for Investigations
Alright, class. Take your seats.
It’s 3 PM on a Tuesday. An urgent message lands in your inbox from HR, Legal, or maybe even the CISO. The

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.