 Microsoft Sentinel
Fixing the "Account Created and Deleted in Short Timeframe" Analytic Rule
Alright class.
Today it is "Account Created and Deleted in Short Timeframe". The rule pairs a "Delete user" event with an earlier "Add
Topic
Analytic Rules
Microsoft Sentinel analytic rules taken apart and rebuilt: why the templates misfire in production, how to tune them, and KQL rules you can deploy.
33 posts
Microsoft Sentinel
Fixing the "Account Created and Deleted in Short Timeframe" Analytic Rule
Alright class.
Today it is "Account Created and Deleted in Short Timeframe". The rule pairs a "Delete user" event with an earlier "Add
 Microsoft Sentinel
PIM Auditing in Microsoft Sentinel: High Value Detections
Alright class.
Most lessons in this series are usually autopsies. We take a content hub rule, find the line that breaks it, and put it back together properly.
 Microsoft Sentinel
Why KQL Enrichment Actually Works (And Why Your Alerts Are So Much Better With It)
All right class.
You run an analytic rule. It fires (duh). Your SOC analyst opens the incident. They see a CallerIpAddress, a Caller name, and OperationNameValue. Then what?
 KQL
Beauty of Data Visualization in Microsoft Sentinel Using KQL
Welcome back, class.
Tables are useless at scale. You know this already. A thousand rows of sign-in data tell you nothing. A hundred thousand rows of process
 KQL
Fixing Microsoft's Azure Brute Force Detection: Why Their Template Fires Constantly (And What You Should Change)
All right class.
Microsoft ships an out-of-the-box analytic rule for Azure Portal brute force attempts. It looks good on paper. It catches failures. It'
 Microsoft Sentinel
The KQL Playbook (Play #2): Mastering the Matching Game
Alright, class. Welcome back to the KQL playbook.
In our last session, we covered the four core moves of KQL. You learned how to grab a table, filter
 Microsoft Sentinel
Beyond the Basics: Forging Your Own Custom Detections in Defender XDR
Alright, class.
You've started to notice something. Sentinel is the brilliant general in the command tent, seeing the whole battlefield. The actual guards on the walls,
 Microsoft Sentinel
How to Bulk Enable All Sentinel Analytic Rules (The Easy Way)
Alright, class, let's have an honest conversation.
You've just deployed Microsoft Sentinel. You followed the guides. You've connected your data sources from
 Microsoft Sentinel
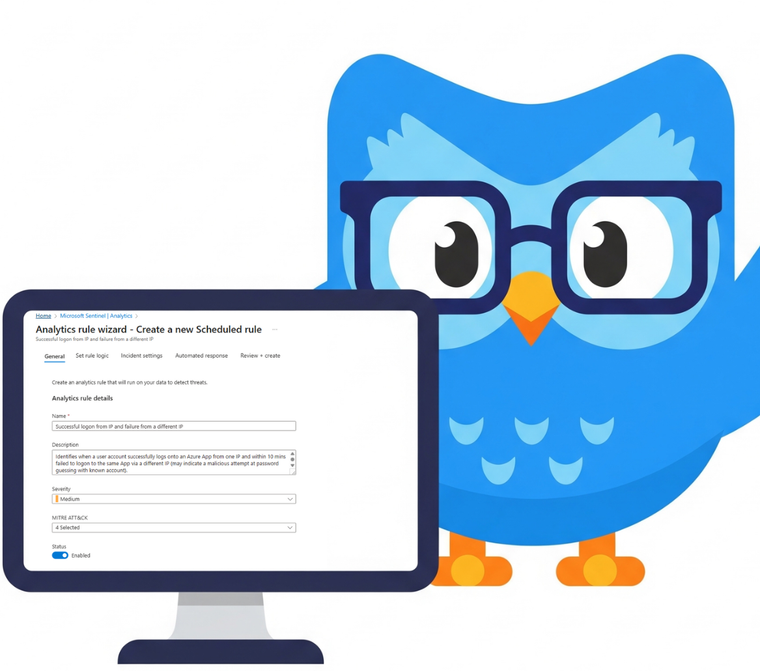
: From Logs to Alerts - Creating Your First Analytic Rule
Welcome back, class! In our last lesson, we successfully turned on the data firehose with Data Connectors. Your Sentinel instance is now collecting logs, which is a fantastic

Get the next post by email
One email per post, plus the KQL Vault. That's the whole deal.